Sandboxing Malware C2 Analysis: Detect Hidden Threats
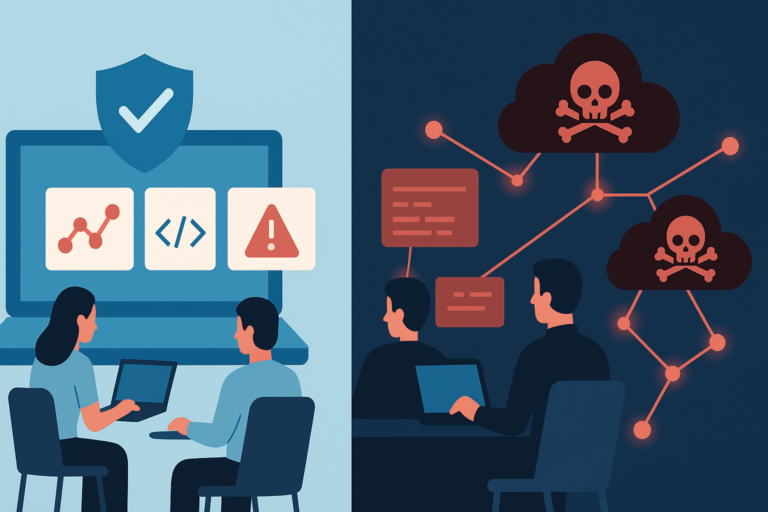
Malware’s command-and-control (C2) behavior can’t be fully understood just by looking at its code. Sandboxing steps in as a way for security teams to watch malware in action, safely. It’s not just about running suspicious files in a locked-down space,…