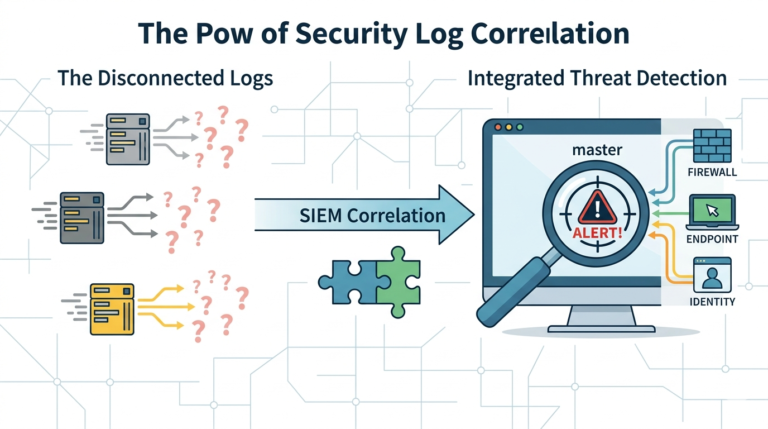
Collecting Correlating Security Logs SIEM: The Key to Better Threat Detection
Collecting correlating security logs SIEM is one of the most effective ways to improve threat detection without increasing…
Collecting correlating security logs SIEM is one of the most effective ways to improve threat detection without increasing…
A SIEM system is a centralized security layer that collects logs, events, and alerts from across networks, endpoints,…
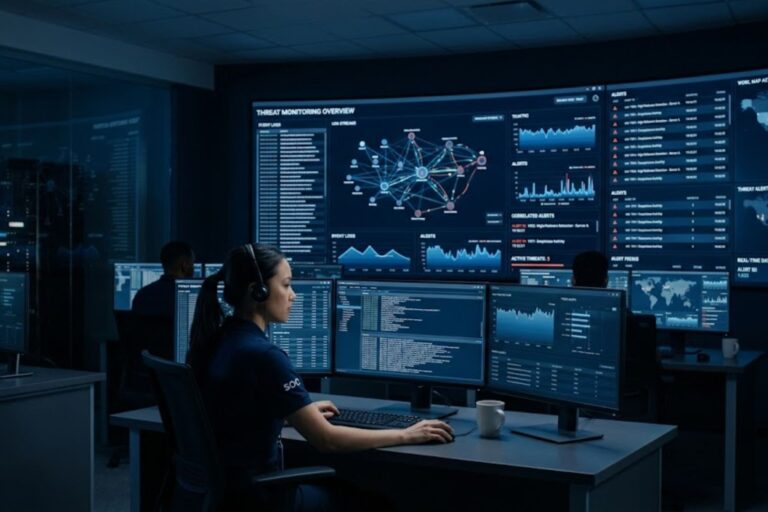
SIEM is a centralized security system that collects, normalizes, and correlates logs to detect threats across complex environments.…

Threat modeling tools comparison Microsoft OWASP comes down to one question: which tool will your team actually keep…

Integrating threat modeling SDLC practices works best when security becomes part of everyday engineering, not a one-time audit…

VAST, which stands for Visual, Agile, and Simple Threat modeling, enables organizations to identify and manage security risks…