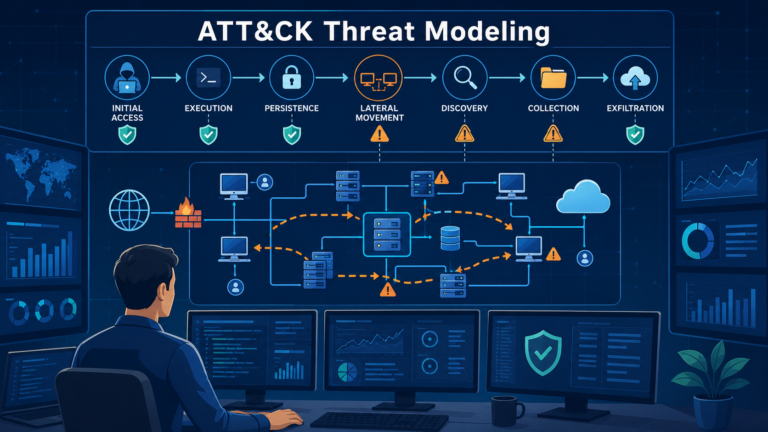
Using ATT&CK Threat Modeling Process to Strengthen Network Threat Detection
Modern cyber threats evolve quickly, making it difficult to rely on assumptions alone. Using ATT&CK threat modeling process…
Modern cyber threats evolve quickly, making it difficult to rely on assumptions alone. Using ATT&CK threat modeling process…
ATT&CK control mapping helps organizations see whether their security tools can detect and respond to real attacker behavior.…
The MITRE ATT&CK matrix helps security teams understand how attackers behave by organizing tactics, techniques, sub techniques, and…
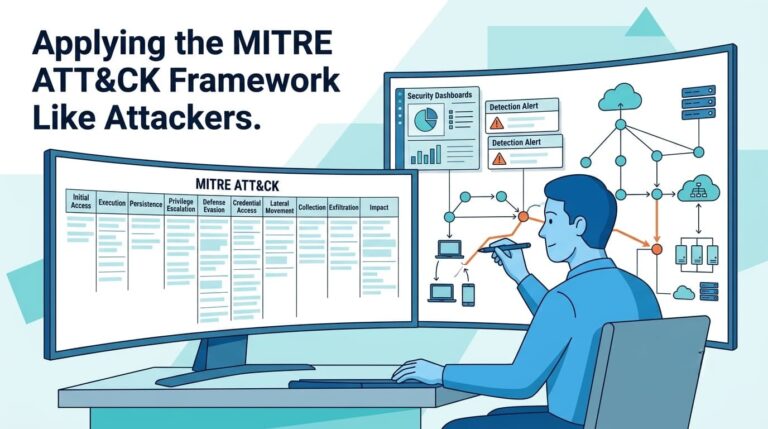
MITRE ATT&CK provides a shared language for cyber defense. It’s a framework that lets you view your network…
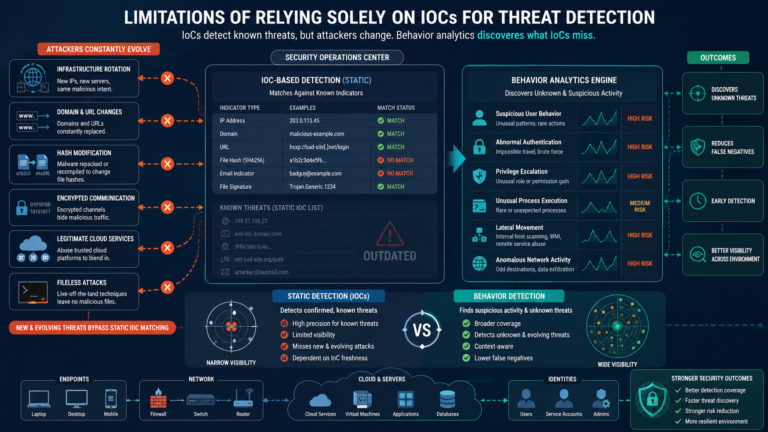
The limitations relying solely IoCs become clear as attackers constantly change infrastructure, tools, and techniques faster than static…
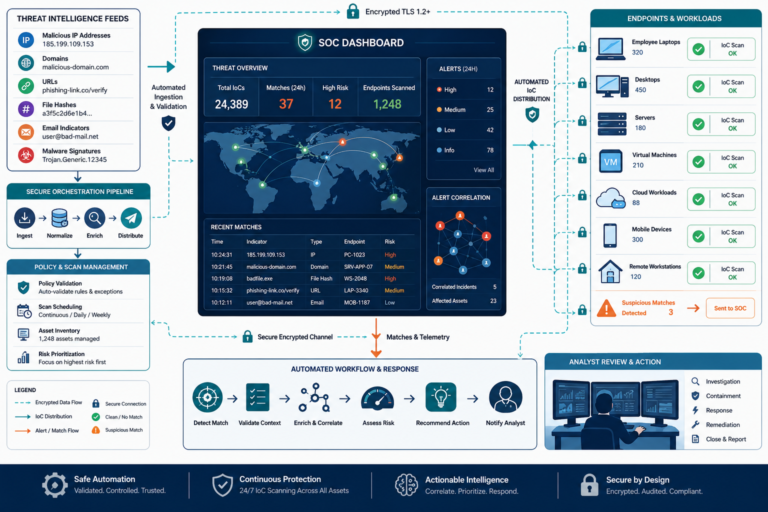
Automating IoC scanning network endpoints helps security teams detect known threats across distributed infrastructure faster while maintaining consistent…