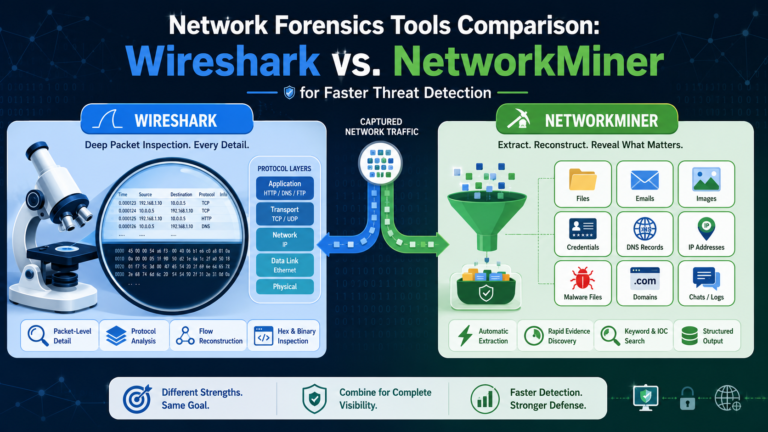
Network Forensics Tools Comparison Wireshark NetworkMiner for Faster Threat Detection
Choosing between Wireshark and NetworkMiner can significantly impact the speed and accuracy of a security investigation. In this…
Choosing between Wireshark and NetworkMiner can significantly impact the speed and accuracy of a security investigation. In this…
Identifying attacker activity network logs. Attackers leave a trail, but you need to connect the dots across DNS…
How do we reconstruct events from network data? Our “Reconstructing Events Network Data Analysis Guide” outlines the method.…
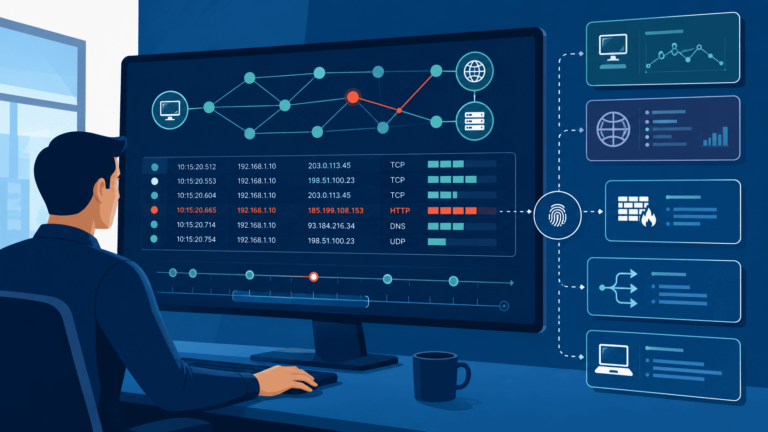
Network traffic analysis helps investigators trace suspicious activity, find affected systems, and preserve evidence for forensic review. NIST…
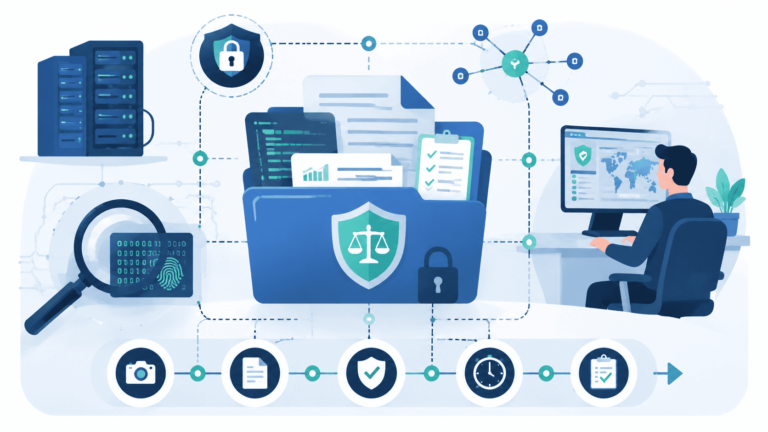
Network evidence is strongest when its collection, scope, integrity, and source are documented from start to finish. For…
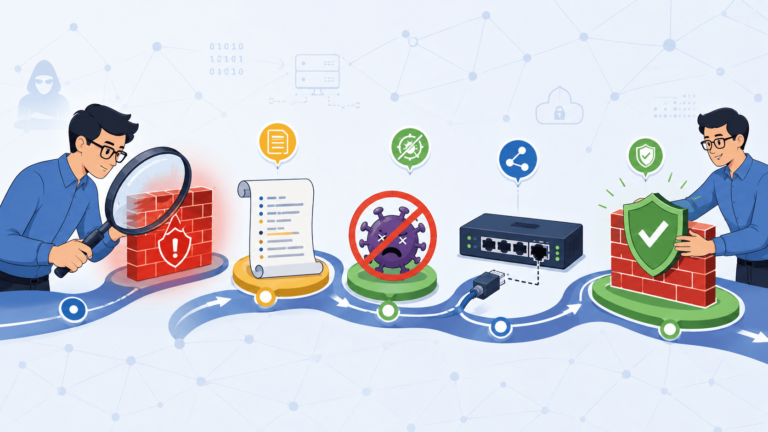
Network forensics follows a clear process to preserve, collect, review, and report network evidence so findings can stand…