How to Run a Network Forensics Investigation
Network forensics investigation shows what happened, when it happened, how the attack unfolded, and which systems or data…
Network forensics investigation shows what happened, when it happened, how the attack unfolded, and which systems or data…
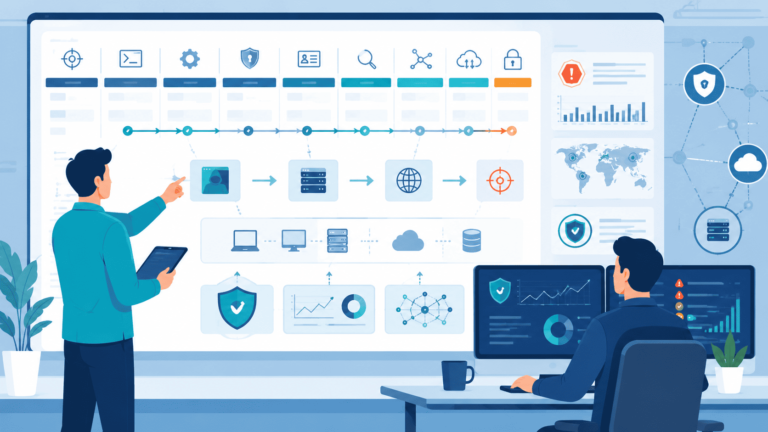
Adversary emulation plans let security teams test whether their defenses can detect the same tactics, techniques, and procedures…
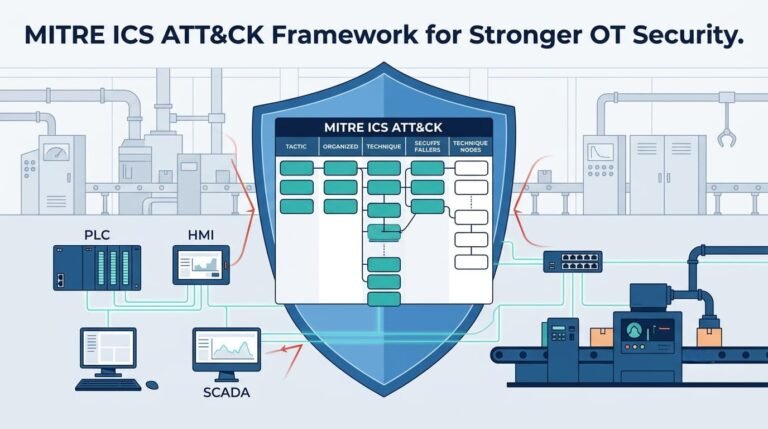
It’s a toolkit for fighting hackers who target factories and power plants. I learned its real value on…

Cyberattacks often begin long before exploitation, making MITRE PRE ATT&CK reconnaissance planning an essential part of a proactive…

Understanding ATT&CK Navigator tool visualization usage helps security teams transform complex detection logic into a clear, actionable view…

Developing ATT&CK based detection rules helps security teams detect real threats by focusing on adversary behavior instead of…