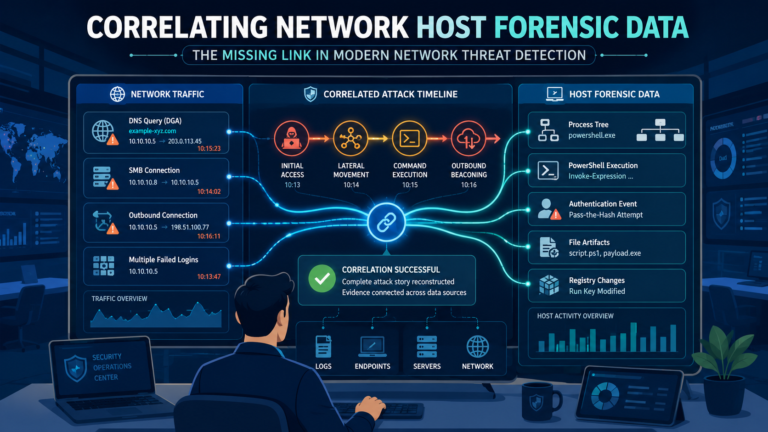
Correlating Network Host Forensic Data: The Missing Link in Modern Network Threat Detection
Modern attacks rarely leave evidence in just one place. While network monitoring shows how threats move, endpoint forensics…
Modern attacks rarely leave evidence in just one place. While network monitoring shows how threats move, endpoint forensics…
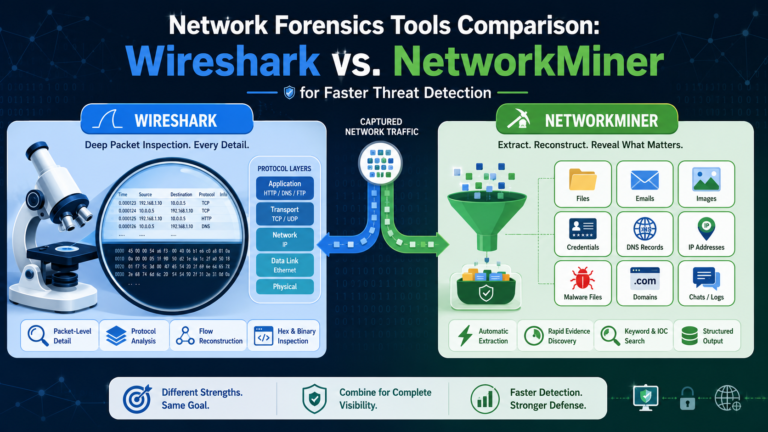
Choosing between Wireshark and NetworkMiner can significantly impact the speed and accuracy of a security investigation. In this…
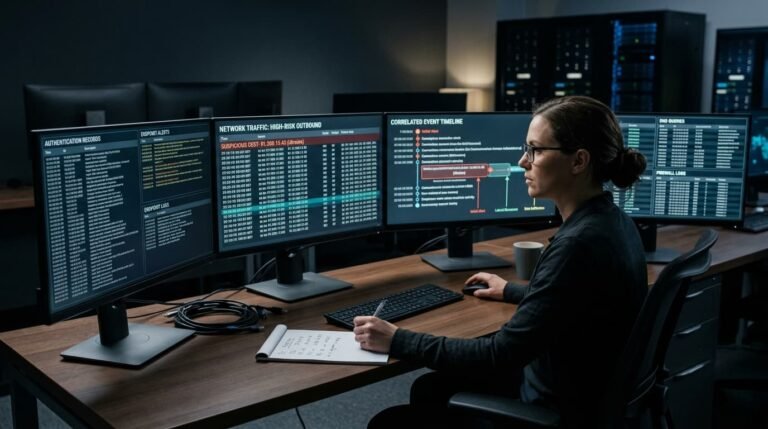
Identifying attacker activity network logs. Attackers leave a trail, but you need to connect the dots across DNS…
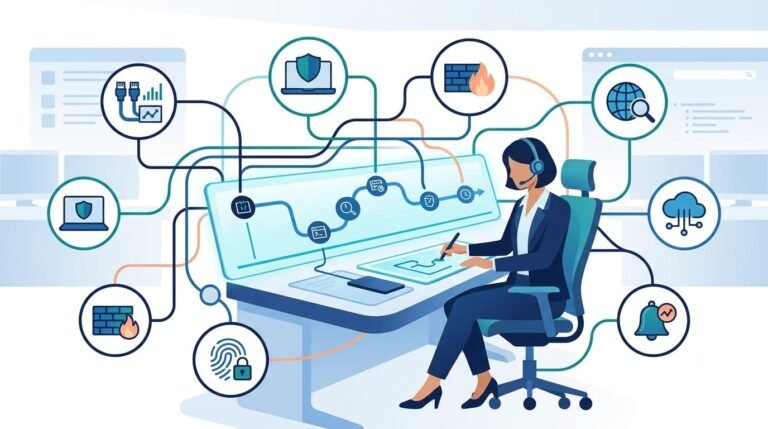
How do we reconstruct events from network data? Our “Reconstructing Events Network Data Analysis Guide” outlines the method.…
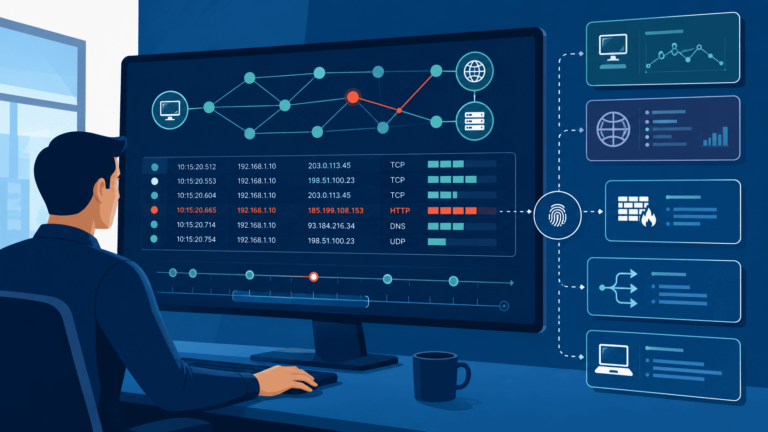
Network traffic analysis helps investigators trace suspicious activity, find affected systems, and preserve evidence for forensic review. NIST…
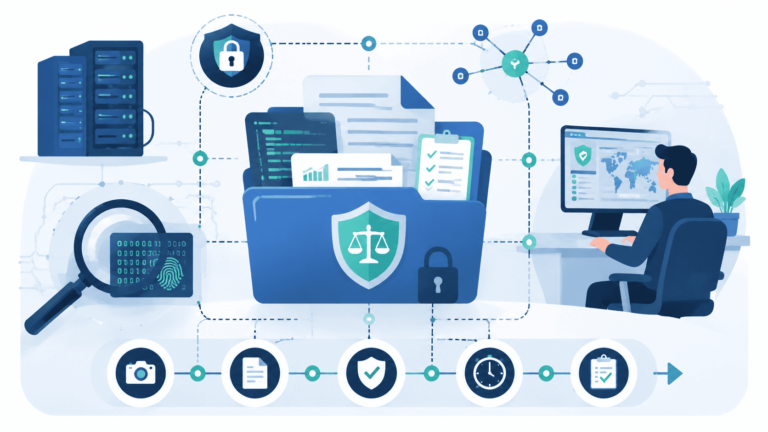
Network evidence is strongest when its collection, scope, integrity, and source are documented from start to finish. For…