
Developing ATT&CK Based Detection Rules for Smarter Network Threat Detection
Developing ATT&CK based detection rules helps security teams detect real threats by focusing on adversary behavior instead of…
Developing ATT&CK based detection rules helps security teams detect real threats by focusing on adversary behavior instead of…

Evaluating security tool ATT&CK coverage helps organizations measure detection effectiveness against proven adversary techniques instead of relying on…

Threat hunting becomes far more effective when it’s guided by evidence instead of assumptions. Using ATT&CK for threat…
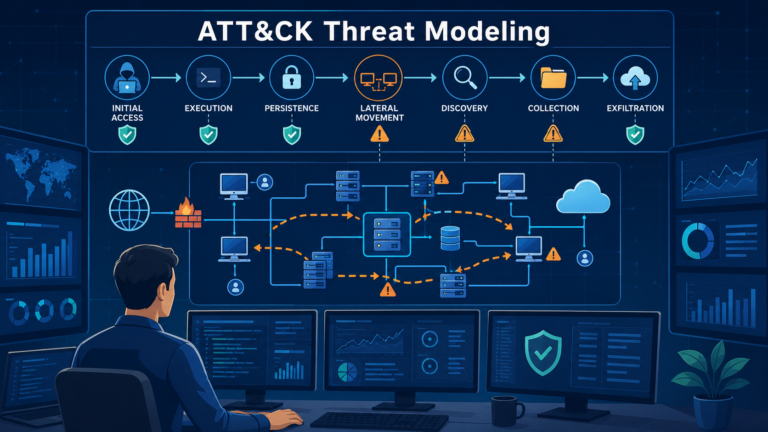
Modern cyber threats evolve quickly, making it difficult to rely on assumptions alone. Using ATT&CK threat modeling process…

ATT&CK control mapping helps organizations see whether their security tools can detect and respond to real attacker behavior.…

The MITRE ATT&CK matrix helps security teams understand how attackers behave by organizing tactics, techniques, sub techniques, and…