Skip to content
Network Threat Detection
  • Home
  • About
  • Blog
  • Contact
  • Features
    • Analysis, Intelligence & Context (Provider Focus)
    • Incident Response & Remediation
    • Network Threats & Adversaries
    • NTD Data Sources & Collection
    • NTD Operational Aspects & Practices
    • NTD Technologies & Methods
    • NTD Tools & Platforms (Provider Focus)
Network Threat DetectionNetwork Threat Detection
  • Home
  • About
  • Blog
  • Contact
  • Features
    • Analysis, Intelligence & Context (Provider Focus)
    • Incident Response & Remediation
    • Network Threats & Adversaries
    • NTD Data Sources & Collection
    • NTD Operational Aspects & Practices
    • NTD Technologies & Methods
    • NTD Tools & Platforms (Provider Focus)
Request a demo
Network Threat DetectionNetwork Threat Detection
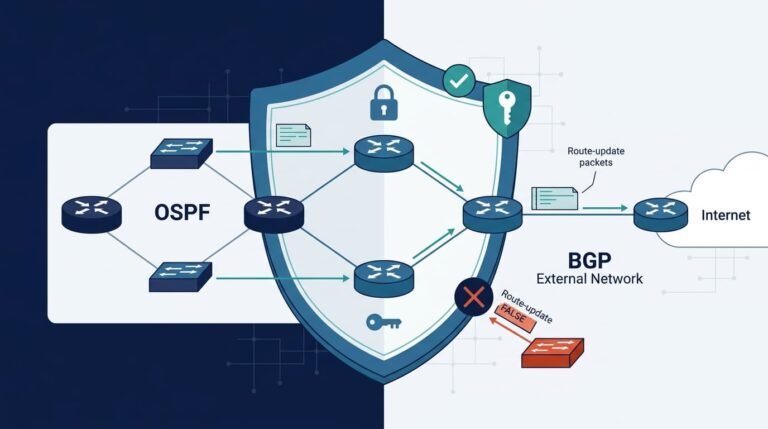
Diagram illustrating securing routing protocols OSPF BGP authentication to block false external route updates.
  • October 15, 2026
  • Router and Switch Security Best Practices, 6. Network Infrastructure & Controls

Securing Routing Protocols: OSPF and BGP Authentication

Securing routing protocols OSPF BGP authentication helps block unauthorized peers and false route updates. OSPF and BGP need…
Read MoreSecuring Routing Protocols: OSPF and BGP Authentication
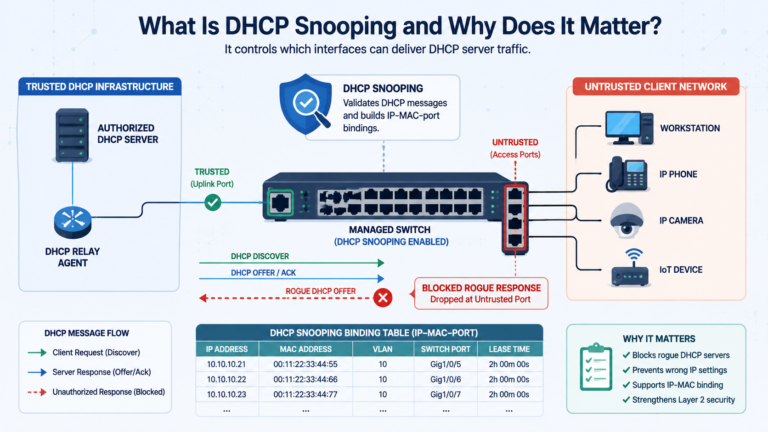
DHCP snooping configuration benefits security showing trusted and untrusted DHCP network paths
  • October 14, 2026
  • Router and Switch Security Best Practices

DHCP Snooping Configuration Benefits Security Tips 

DHCP snooping configuration benefits security by validating DHCP traffic, blocking unauthorized server responses, and creating IP-MAC-port bindings for…
Read MoreDHCP Snooping Configuration Benefits Security Tips 
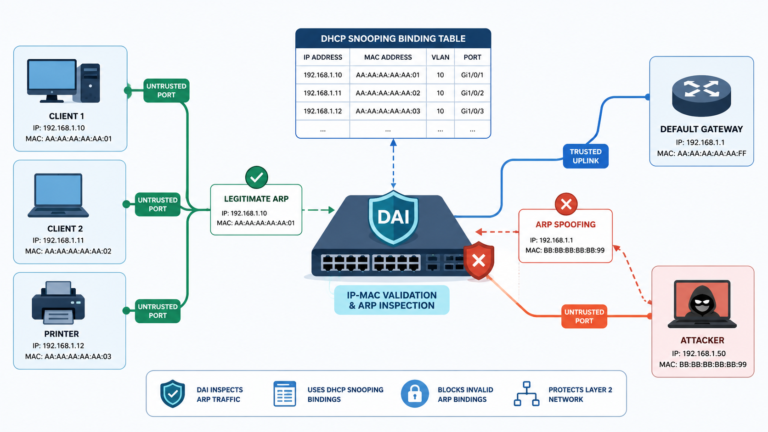
Preventing ARP spoofing dynamic ARP inspection with DHCP snooping and IP-MAC validation
  • October 13, 2026
  • Router and Switch Security Best Practices

Preventing ARP Spoofing Dynamic ARP Inspection Guide 

Preventing ARP spoofing dynamic ARP inspection starts by checking ARP traffic against trusted IP-MAC bindings before forged mappings…
Read MorePreventing ARP Spoofing Dynamic ARP Inspection Guide 
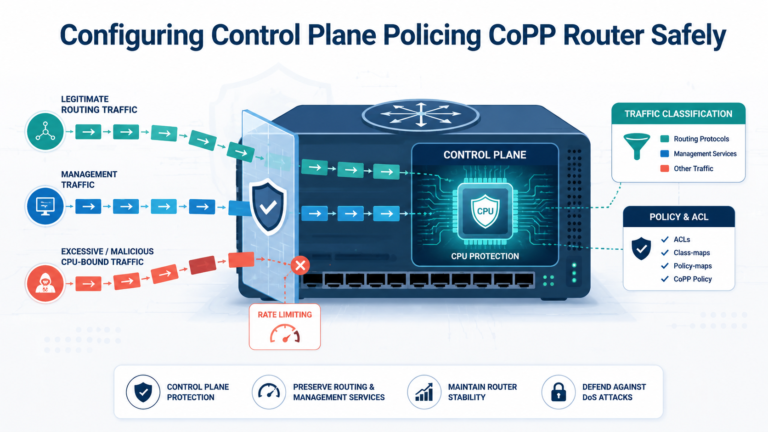
Configuring control plane policing CoPP router illustration showing CPU protection and rate-limited traffic. 
  • October 12, 2026
  • Router and Switch Security Best Practices

Configuring Control Plane Policing CoPP Router Safely 

Configuring control plane policing CoPP routers helps protect the route processor from excessive CPU-bound traffic while keeping routing…
Read MoreConfiguring Control Plane Policing CoPP Router Safely 
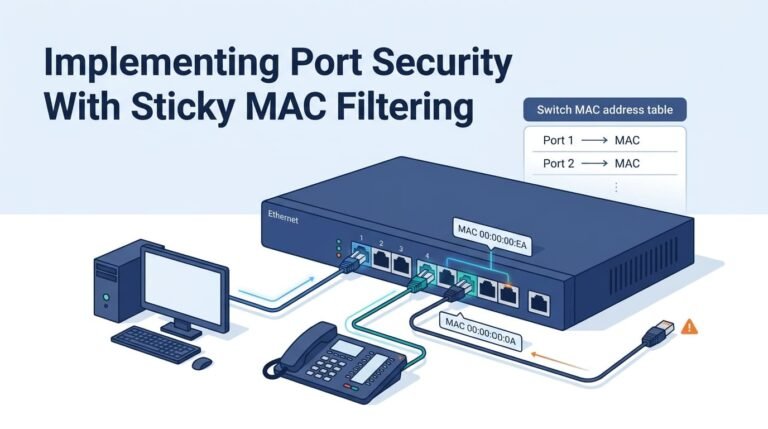
Diagram showing implementing port security mac filtering sticky mac on a switch with connected PC and IP phone.
  • October 11, 2026
  • Router and Switch Security Best Practices, 6. Network Infrastructure & Controls

Implementing Port Security With Sticky MAC Filtering

Implementing port security mac filtering sticky mac helps a switch learn approved MAC addresses and limit access on…
Read MoreImplementing Port Security With Sticky MAC Filtering
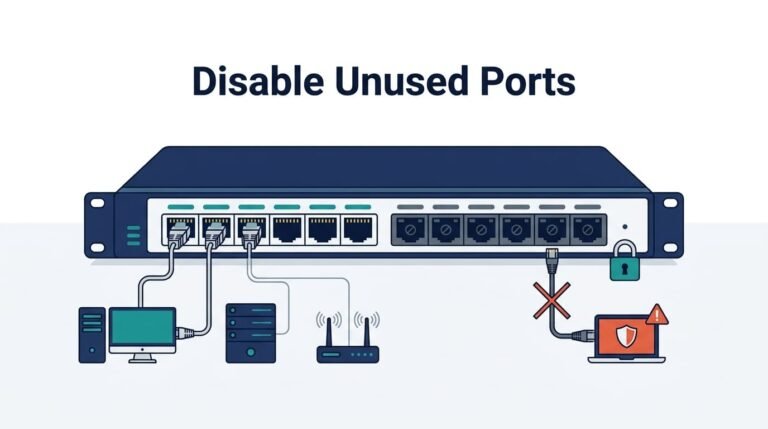
Network switch diagram showing disabling unused switch ports interfaces to block unauthorized devices.
  • October 10, 2026
  • Router and Switch Security Best Practices, 6. Network Infrastructure & Controls

Disabling Unused Switch Ports Interfaces: A Guide

Disabling unused switch ports interfaces reduces open access points and limits unauthorized device connections. Unused ports can give…

Read MoreDisabling Unused Switch Ports Interfaces: A Guide
Prev
1 2 3 4 5 6 7 … 95
Next
Network Threat Detection

NetworkThreatDetection

Threat modeling untuk SOC teams, analysts & CISOs. Stay ahead of attackers.

Request a demo →
  • NTD Technologies & Methods
  • NTD Data Sources & Collection
  • Network Threats & Adversaries
  • Incident Response & Remediation
  • NTD Tools & Platforms (Provider Focus)
  • NTD Operational Aspects & Practices
  • Analysis, Intelligence & Context (Provider Focus)
  • About
  • Contact
  • Privacy Policy
  • Terms & Conditions

© 2026 NetworkThreatDetection.com. All rights reserved.