Avatar photo

Joseph M. Eaton

Hi, I'm Joseph M. Eaton — an expert in onboard threat modeling and risk analysis. I help organizations integrate advanced threat detection into their security workflows, ensuring they stay ahead of potential attackers. At networkthreatdetection.com, I provide tailored insights to strengthen your security posture and address your unique threat landscape.

Finding Ghosts in the Wires: Memory Forensics Network Connections Analysis That Exposes Hidden Threats

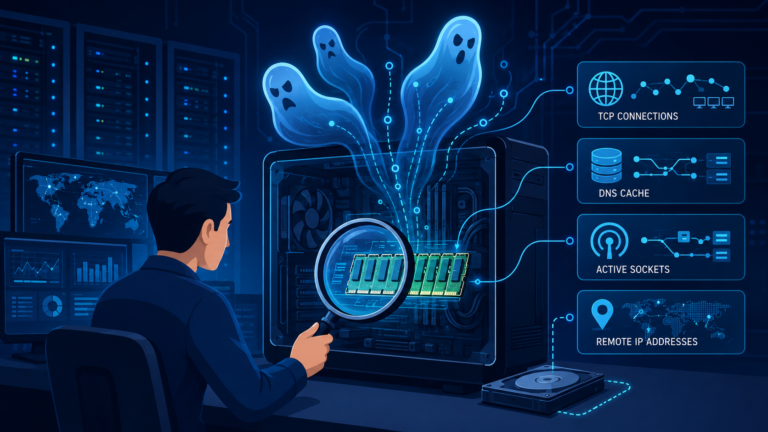
Illustration showing memory forensics network connections analysis on a laptop screen. 

 Attackers rarely leave obvious clues, but every active network connection creates valuable evidence inside system memory. Through memory forensics network connections analysis, investigators can uncover hidden backdoors, suspicious remote sessions, and command-and-control communication that never appears on disk.  Combined with…

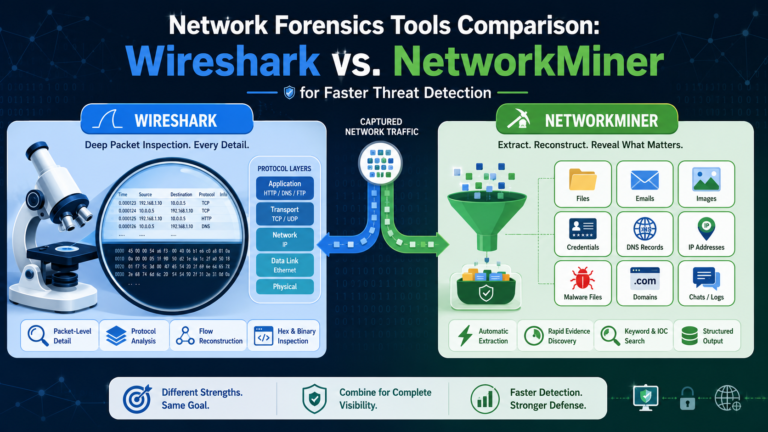
Network Forensics Tools Comparison Wireshark NetworkMiner for Faster Threat Detection

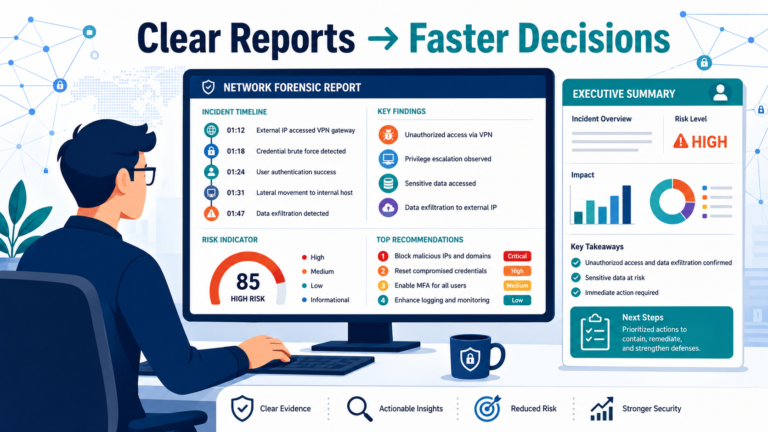
Network forensics tools comparison Wireshark NetworkMiner showing deep packet analysis and evidence extraction. 

Choosing between Wireshark and NetworkMiner can significantly impact the speed and accuracy of a security investigation. In this network forensics tools comparison wireshark networkminer, you’ll discover how each tool approaches traffic analysis, evidence collection, and incident response.  Whether you’re investigating…

Analyzing Network Traffic for Forensic Investigation

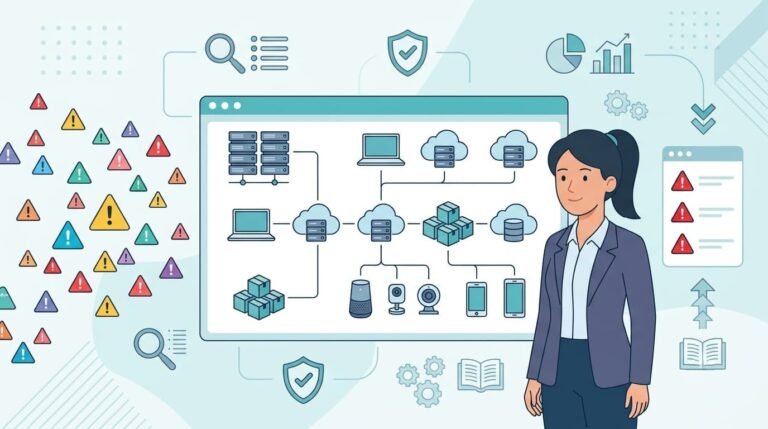
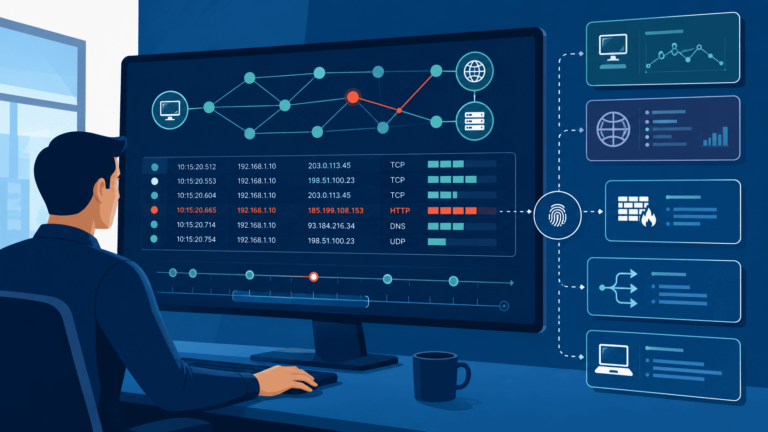
Analyst monitoring dashboard for analyzing network traffic forensic investigation with flagged alerts.

Network traffic analysis helps investigators trace suspicious activity, find affected systems, and preserve evidence for forensic review. NIST SP 800-86 identifies network traffic as one of the major data-source categories used in computer and network forensics. For Network Threat Detection,…